REMOTE WORK SECURITY
Working remotely on public Wi-Fi: a practical security checklist
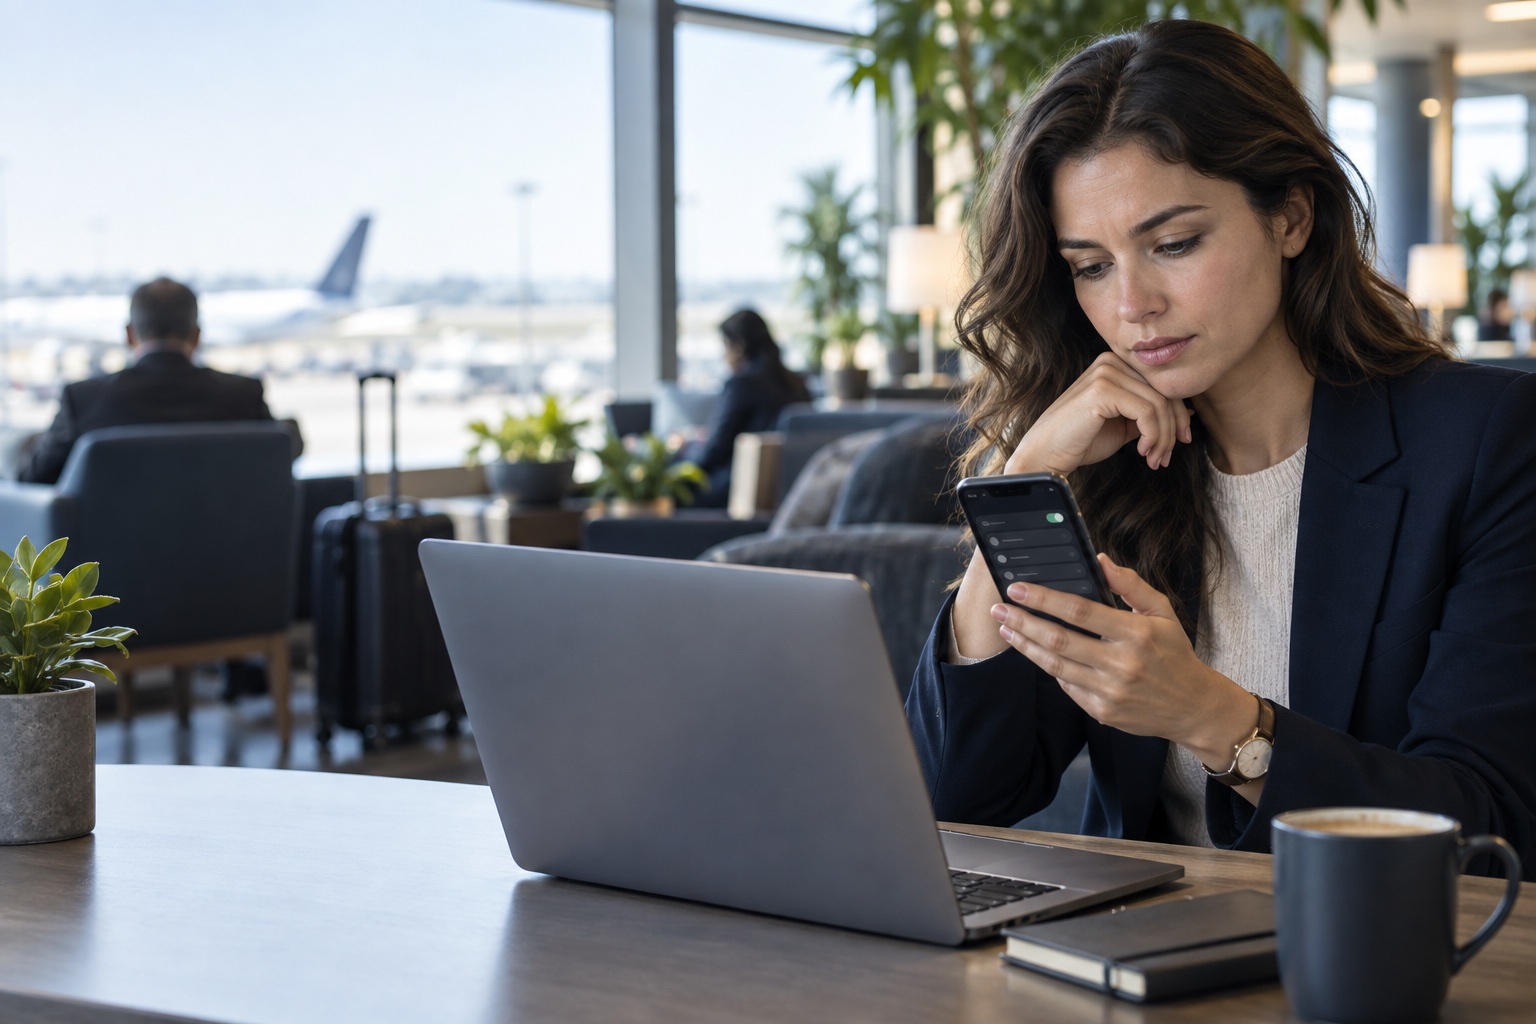
Public Wi-Fi is not automatically unsafe, but the wrong network, a deceptive sign-in page or a careless work session can still expose accounts and confidential information. Use a short decision check before connecting.
Start with the employer's rule, not a generic travel tip
Before using a café, airport, hotel or co-working network, check the organisation's remote-work and device policy. It may require a managed device, an approved VPN, a specific multi-factor method or a mobile connection for certain data. A technically available network is not necessarily an approved route for work.
The U.S. National Institute of Standards and Technology advises teleworkers to follow their organisation's security policy, keep devices patched and use the employer's VPN when one is provided. If the approved connection fails or a login prompt looks unusual, contact the official help desk rather than changing a security control to finish a task quickly.
Confirm the network before you send any traffic
Ask staff for the exact network name and sign-in method. Similar names can be created by another person, and a familiar venue name is not proof that the network belongs to the venue. Disable automatic joining so the device does not reconnect to a remembered network without a fresh check.
A captive portal may appear before normal internet access works. If a work VPN cannot connect until that page is completed, follow the employer's documented process. Do not casually turn off a required VPN or install a certificate, browser extension or profile offered by an unexpected page.
- Verify the network name and login instructions with venue staff.
- Forget the network after the session and keep automatic joining disabled.
- Treat requests to install software, profiles or certificates as a stop signal.
- Use a verified mobile hotspot instead when the task or policy requires a more controlled connection.
Understand what HTTPS does — and what it does not do
The U.S. Federal Trade Commission notes that widespread HTTPS encryption makes public Wi-Fi safer than it once was. Check that the site uses HTTPS, keep the browser and operating system updated, use strong unique passwords and enable multi-factor authentication.
HTTPS protects the connection to a site; it does not prove the site itself is honest. A phishing page can also use HTTPS. Open sensitive services from a saved bookmark or a known address, inspect the domain carefully and stop if a login page, approval request or multi-factor prompt is unexpected.
Protect the email account behind your applications →Recognise risky remote-access requests →
Move sensitive work to a more appropriate connection
Delay payroll changes, identity-document uploads, banking, production administration and confidential client work if the connection or environment cannot be verified. A mobile hotspot is often more controlled than an unknown shared network, but it still needs a strong hotspot password, current device software and permission under the employer's policy.
Physical privacy matters too. A secure connection does not prevent shoulder surfing, overheard calls or an unattended laptop. Use the screen lock, avoid confidential conversations in open spaces and store files only in approved systems.
Check personal-device boundaries →Secure the network you control at home →
Use this public Wi-Fi decision check
- Confirm that the device, network type and VPN route are allowed by the employer.
- Verify the exact network name and captive-portal method with venue staff.
- Install pending operating-system, browser and security updates before travelling.
- Use HTTPS, a password manager and multi-factor authentication, but still inspect the domain.
- Move highly sensitive work to an approved mobile or private connection.
- Lock the screen, protect conversations and keep work files in approved storage.
- Report unexpected prompts or account activity through the official support route.
Build a repeatable remote-work routine →Browse current checked roles →
Follow RemoRoute
Choose the updates that suit you.
Use Telegram for fast role updates and LinkedIn for research, practical articles and selected opportunities.