JOB SEARCH SECURITY
How to secure your job-search email against fake recruiter phishing
Your email often resets every job-board account you use. A unique sign-in, phishing-resistant verification and careful recruiter-link checks reduce the damage one message can cause.
Protect email first because it unlocks other accounts
Job-search email contains CVs, interview times, application links and messages from unfamiliar people. It may also be the recovery address for job boards, cloud storage and professional profiles. If someone controls it, they can reset other passwords, impersonate you or use real application context to make a phishing message more convincing.
Consider a separate email address for applications so recruitment traffic is easier to review and a breach does not expose unrelated personal correspondence. Separation is not a complete security control, but it reduces unnecessary exposure and makes suspicious forwarding rules or messages easier to spot.
Use a unique password and stronger multi-factor authentication
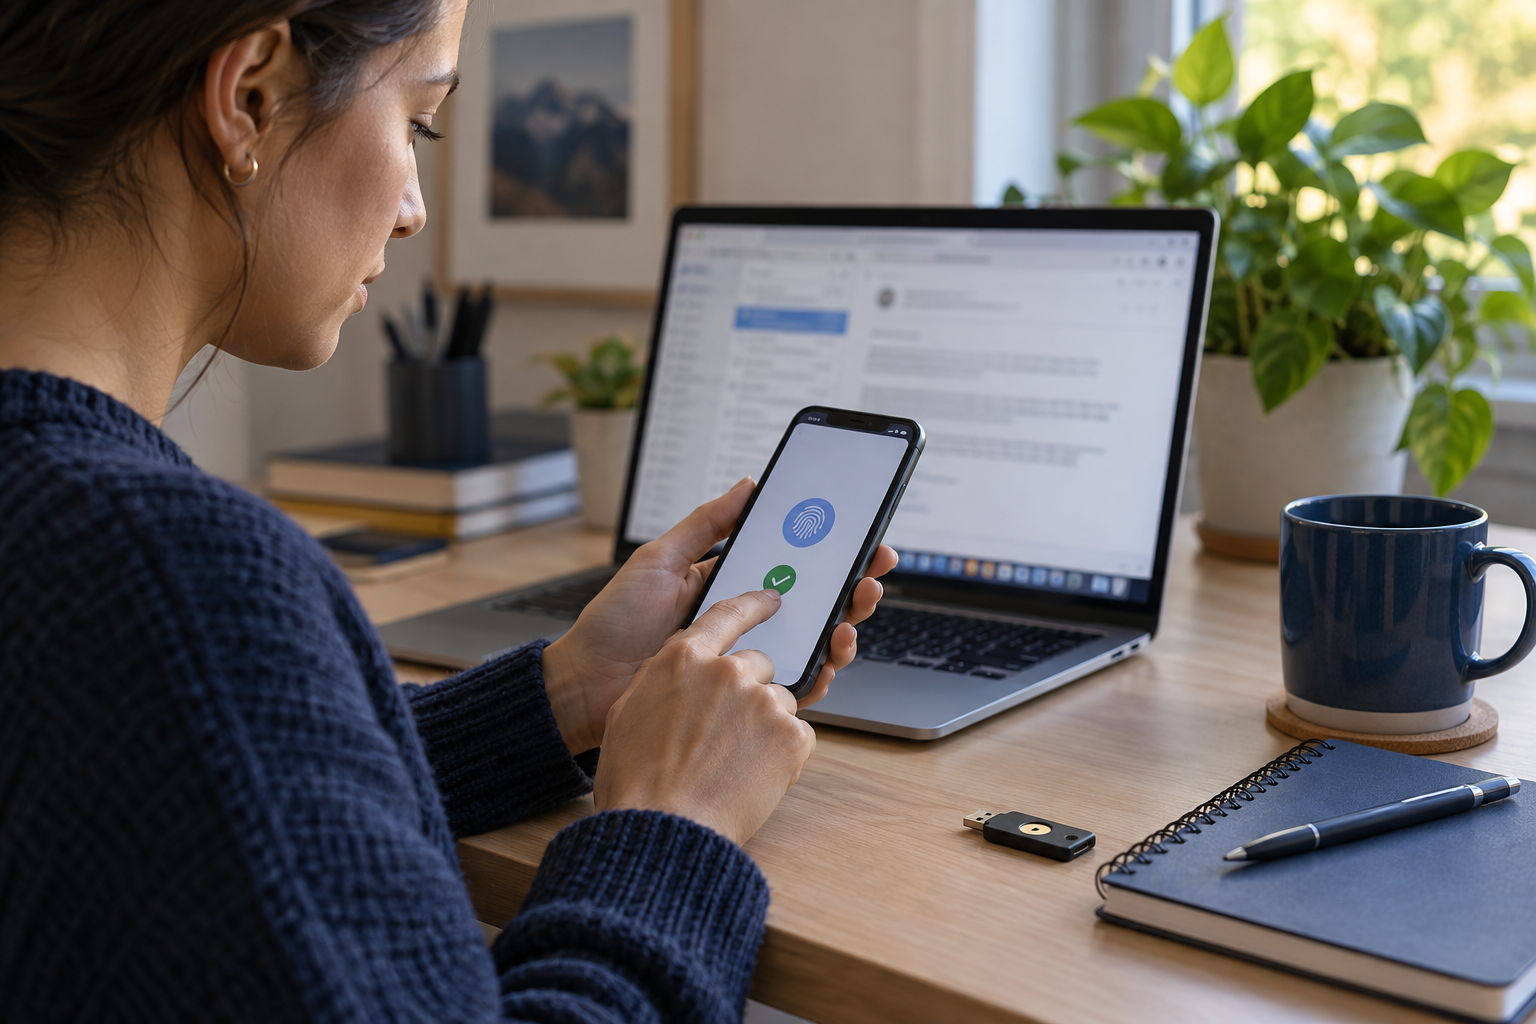
Use a long password that is not reused anywhere else, ideally stored in a trusted password manager. Turn on multi-factor authentication and save recovery codes somewhere separate from the inbox. Review the recovery phone number, backup email and signed-in devices so an old device or address cannot quietly restore access.
CISA describes phishing-resistant authentication as the strongest option. A security key or passkey can resist the fake sign-in pages that steal passwords and one-time codes. If those options are unavailable, app-based approval with number matching is generally stronger than relying only on SMS, which is not phishing-resistant.
Inspect the recruiter route before signing in
A real application can use an external applicant-tracking or assessment provider, so an unfamiliar domain is not automatically malicious. Verify it from the employer's official careers page or by contacting the company through details you found independently. Check the full sender address and destination domain, not only the logo, display name or button label.
Be especially cautious when an unexpected message creates urgency, asks you to sign in again, requests identity or banking information before a verified process, or moves immediately to a private chat. Do not upload a CV, passport or background-check document merely because a page resembles a known service.
Recover safely after a suspicious click
If you entered credentials on a suspicious page, open the email provider through a trusted bookmark or by typing its address yourself. Change the password, sign out unknown sessions, remove unfamiliar recovery methods and check forwarding rules, filters and sent mail. Reset any other account that reused the same password.
If a passkey, security key or approved-device prompt protected the account and you did not approve the sign-in, still review the security log. Tell the genuine employer if its name or vacancy was copied, report the message to your provider and preserve the sender address, headers and destination URL for the report.
Check whether the message is part of an equipment-payment scam →
Use this job-search account checklist
- Use a unique email password and store it in a trusted password manager.
- Enable a passkey or security key where available and keep recovery codes offline.
- Review recovery details, active sessions and forwarding rules regularly.
- Confirm recruiter and assessment domains from the employer's official website.
- Open important accounts from a bookmark instead of an email sign-in button.
- Do not approve an unexpected MFA prompt or share a one-time code.
- Change reused credentials and review all sessions immediately after a suspicious sign-in.
Read RemoRoute's privacy and security approach →Browse current checked roles →
New roles first
Use the board for live opportunities.
Telegram is the fastest route for new RemoRoute role updates. The site is where we keep the context and practical guidance.
Join Telegram ↗