AI & WORK
Before you paste work into an AI tool: a confidential-data checklist
An AI assistant can help organise or rewrite material, but a useful output does not cancel confidentiality, privacy or security obligations. Decide what the tool is allowed to receive before you paste the first line.
Treat the prompt as a disclosure to another service
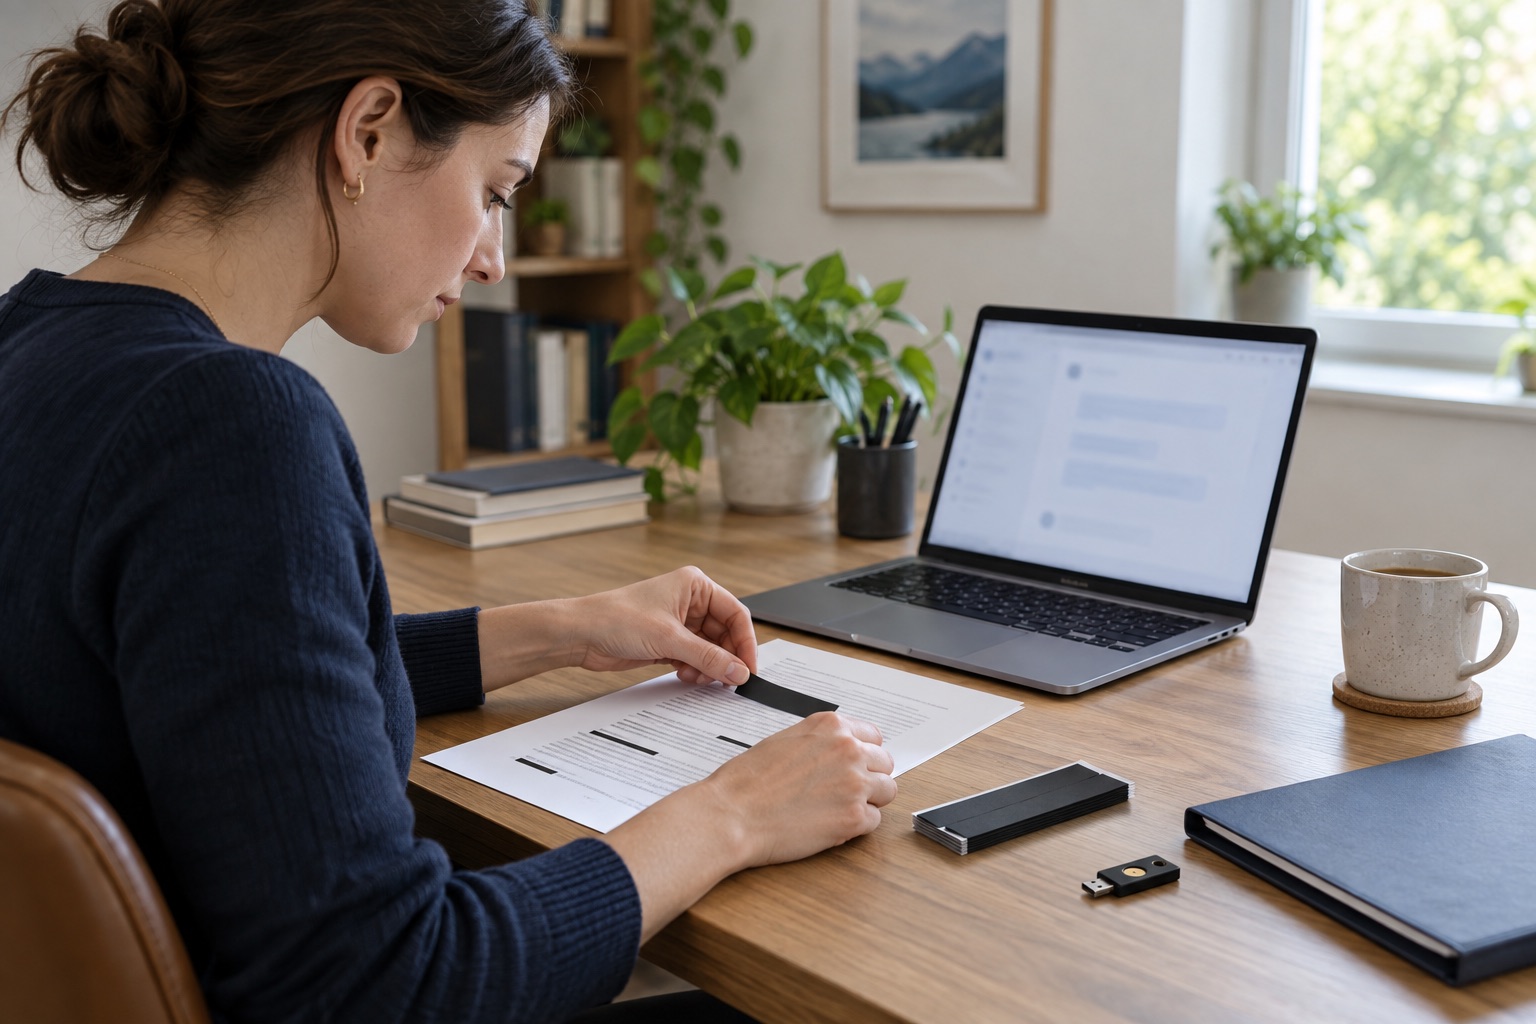
Text pasted into a public AI tool leaves the document or system where it was originally stored. The service provider may process and retain the prompt under its product terms, privacy notice, account settings and organisational agreement. Do not assume a paid account, a private browser window or a request to ‘keep this confidential’ changes those rules.
The UK National Cyber Security Centre recommends not including sensitive information in queries to public large-language models and not submitting a query that would cause problems if it became public. Read the current terms and your employer's approved-use policy before using a tool for work.
Identify the data before deciding whether to use AI
A document can contain several risk categories at once: names and contact details, customer records, health or financial information, confidential commercial plans, unreleased code, security credentials, legal material or information supplied under a non-disclosure agreement. Removing the company name may not remove the identity of a person or project.
The ICO's AI and data-protection guidance emphasises that organisations remain responsible for personal-data processing involving AI. OWASP also lists personal, financial, health, credential, legal and confidential business data as sensitive information that can be exposed through LLM applications.
Use the approved tool and the minimum necessary context
Check whether the organisation provides an approved enterprise tool, which account must be used, whether prompts are retained or used for model improvement, where data is processed and which integrations the tool can access. An approved tool may have stronger controls, but it is still subject to the policy and access rules configured by the organisation.
Give the smallest amount of information needed for the task. Replace real names, account numbers, dates, internal URLs and unique project details with neutral placeholders. Summarise a structure instead of uploading the original file when possible, and never place passwords, API keys, session tokens or private keys in a prompt.
Review the output before it becomes work product
Generated text can be inaccurate, incomplete or based on an incorrect interpretation of the prompt. Verify facts, calculations, citations and code before relying on the result. Do not let the tool invent customer statements, performance metrics, legal conclusions or security decisions.
Also check whether the output reproduces information that should not appear in the final document. Copy only the reviewed result into the authorised work system, preserve required records and make sure a responsible person—not the AI tool—owns the final decision.
Use this workplace AI data checkpoint
- Confirm that the AI service and account are approved for the specific work task.
- Read the current retention, training, sharing and access settings that apply to the account.
- Classify the material for personal data, client confidentiality, intellectual property and security secrets.
- Remove names, identifiers, credentials, internal links and unique details that are not necessary.
- Prefer a short anonymised summary over uploading the original document or conversation.
- Verify every material fact and inspect the output for accidental disclosure before reuse.
- If the policy or permission is unclear, stop and ask the data owner, manager or security contact.
Protect the accounts used during your job search →Browse current checked roles →
Follow RemoRoute
Choose the updates that suit you.
Use Telegram for fast role updates and LinkedIn for research, practical articles and selected opportunities.